When Chrome blocks HTTP resources on an HTTPS page, it shows a 'Load unsafe scripts' warning. On modern Chrome the address bar padlock is gone, and the allow option now lives in Site settings. Here is the current procedure on desktop and Android.
Allowing unsafe scripts is fine on a page you trust. Skip it on banking, checkout, or login pages, where the warning exists for a real reason.
In this guide, I have covered:
Contents
How to Load Unsafe Scripts in Chrome
Chrome blocks scripts served over plain http:// on an HTTPS page. You’ll see a “Load unsafe scripts” warning. The old shield icon is gone. The allow control now lives in Site settings.
- Open the HTTPS page that is blocking the scripts.
- Click the Tune icon
 on the left side of the URL bar.
- In the popup, click Site settings. A new tab opens with that site's permission list.
- Scroll to the Permissions section and find Insecure content.
- Click the dropdown next to it and switch it from Block (default) to Allow.
- Return to the original tab and refresh the page. The previously blocked scripts, images, or styles now load.
You’ll know it worked when the “Not secure” or “Loaded over an insecure connection” indicator disappears from the address bar, and the page renders the missing images, scripts, or styles. If nothing changes, make sure you selected Allow rather than Ask, and reload the tab.
Why Chrome Shows the “Load Unsafe Scripts” Warning
Chrome shows this warning because of mixed content protection. A page is served over https:// but pulls scripts, styles, images, or iframes from http://, an attacker on the network can swap those insecure files and read anything you submit on the page. To stop that, Chrome blocks the unsafe requests by default and surfaces the prompt you are looking at. The older broken shield icon on HTTPS pages came from this same check.
The warning can also fire on a trustworthy site if a single plugin, ad network, theme, or extension injects an http:// resource, so even a clean site can trigger it if it has not finished migrating every asset to HTTPS. If you want the full background on what HTTPS actually protects, see our guide on what an SSL certificate does.
How to Allow Insecure Content on Chrome for Android
On Android, you allow insecure content through Chrome’s site permissions list.
- Open Chrome on Android and load the page that is blocking scripts.
- Tap the three-dot menu
 in the top right and choose Settings.
- Tap Site settings.
- Scroll to Permissions and tap Insecure content.
- Tap the site you want to allow, then turn the toggle on so it shows Allowed instead of Blocked.
- Go back and reload the page.
You’ll know it worked when the page reloads without the “Site is not fully secure” banner, and the previously missing scripts or images appear. If you also need to control site wide JavaScript, our guide to enabling or blocking JavaScript on Chrome Android walks through that.
Should You Load Unsafe Scripts?
Only when you trust the page completely. Mixed content blocking exists because an HTTP resource can be tampered with in transit, and any form on that page (search, login, comment, payment) can leak through that hole.

ALERT: If the page is a banking site, a checkout form, a login screen, or anything that asks for a password, card number, or personal information, leave the block in place and leave the site.
For everyday reading, content blogs, and small business sites, allowing the scripts once is usually low risk. Just know that Chrome will keep a small “Not secure” tag on the page while the permission is on, so you can see at a glance that the connection is no longer fully encrypted. The exception that is worth using this on is when you control the page yourself and need to confirm what is being blocked while debugging.
How to Check If a Site’s Connection Is Secure
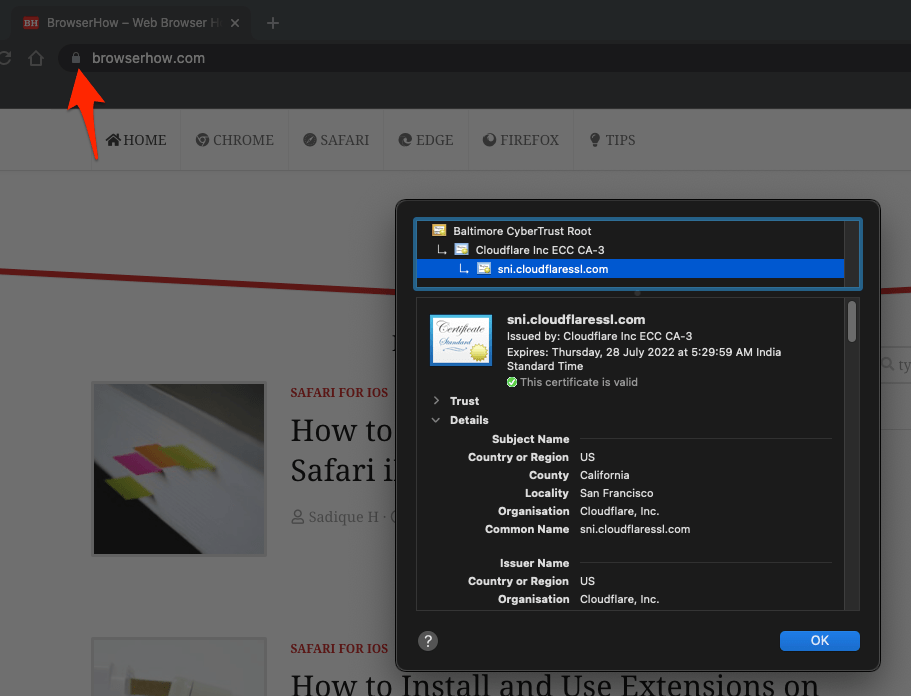
You can verify a site’s certificate without leaving the page. Click the tune icon next to the URL and read the connection status in the popup. If it says “Connection is secure,” the certificate is valid. If it says “Connection is not secure” or “Your connection to this site is not private,” the certificate is missing, expired, or mistrusted, and you should not load unsafe scripts on it.
For deeper certificate details, open Site settings from the same popup and scroll to Privacy and security. You can also walk through Chrome’s full site information and settings panel if you want a full tour.
How Site Owners Can Fix Mixed Content Warnings
If you own the site showing the warning, you can fix it permanently. The fix is rarely to allow the unsafe content; the fix is to remove every http:// reference and serve the page fully over HTTPS.
- Migrate the site to https://. Free certificates are available through Let’s Encrypt, Cloudflare, and most modern hosts.
- Update every link, image, script, stylesheet, and iframe on the page to use https://. Mixed content warnings disappear once nothing references the plain HTTP protocol.
- Find the offending resources in Chrome DevTools. Open More tools > Developer tools > Console and look for “Mixed Content: The page at ‘https://...‘ was loaded over HTTPS, but requested an insecure image ‘http://...‘.” The exact file is listed there.
- Avoid third party ad networks, plugins, or nulled scripts that load resources over HTTP. They are the most common cause of mixed content warnings on otherwise clean sites.
- Run regular server scans with anti-malware tools so an injected script cannot quietly add http:// tags back into your pages.
- Keep your CMS, plugins, and themes updated.
Once every asset is served over HTTPS, reload the page in Chrome and the “Load unsafe scripts” prompt will not come back.
Thank you for great contet! I have some fixes that “need” to be solved.
Glad it helped, Albin!
My WordPress blog gives me error message like This page is tring to load scripts from unauthenticated source.
So, i try to find out why this happen and how to solve it?
And finally comes to this article.
Thank you for posting such great and useful article.
🙂 🙂
I am try but its not working . photoeditingpoint.com
I doubt very much if the BBC iplayer is the problem with Unauthenticated Sources and suspect the problem is something else, in my case
Yes, Brian – that could be a possible issue. Check if the BBC iPlayer is playing through https:// URL using inspect element or source code.
same as above
i would to know what is trying to load and how to remove bearing in mind i am 76
I’d suggest checking your Google Chrome console to understand what exactly is causing the issue here.
Google Toolbar > View > Developer > JavaScript Console